
Microsoft SC-200 : Microsoft Security Operations Analyst

- Exam Code: SC-200
- Exam Name: Microsoft Security Operations Analyst
- Updated: Nov 13, 2026
- Q & A: 435 Questions and Answers
About Microsoft SC-200 Exam
We keep your personal information Confidentiality
Once the candidates buy our products, our SC-200 test practice pdf will keep their personal information from exposing. Our company has a strict information safety system. Our Microsoft SC-200 test prep vce promise candidates the policy of privacy protection, so you can purchase our products without any doubts and hesitation, also you will not receive different kinds of junk emails.
Besides, we still have many other advantages and good service such 7/24 online system service. No matter you have any questions and suggest about our SC-200 training study dumps please feel free to write email to us and contact us by online service.
Instant Download: Upon successful payment, Our systems will automatically send the product you have purchased to your mailbox by email. (If not received within 12 hours, please contact us. Note: don't forget to check your spam.)
Get ready for the Microsoft SC-200 Exam
Microsoft Security Operations Analyst Certification is a professional-level certification that has been designed to recognize individuals with the knowledge and skills necessary to protect enterprise networks from any online threats. While taking the Microsoft SC-200 test, the candidate will be required to have a good understanding of various security threats, malware, and hacker attacks. They will also have to have a deep understanding of different types of firewalls and IDS/IPS systems, as well as how they work together. Candidates should also be aware of network infrastructure devices, such as routers, proxies, and servers involved in implementing an effective security strategy. Another important area that the candidate must cover is risk management techniques used by the enterprise department to identify potential risks and vulnerabilities. The candidate must also know how to effectively monitor internal and external networks for any signs of intrusions or other Cyber crime. The Microsoft SC-200 exam dumps have been designed to provide you with all the knowledge required to pass the Microsoft SC-200 certification exam.
The Microsoft SC-200 exam requires you to have expert knowledge on Windows Server Update Services (WSUS), Group Policy, and Active Directory. Candidates must also possess expert knowledge on System Center Configuration Manager (SCCM) 2007 R2 and Windows Intune.
Reference: https://docs.microsoft.com/en-us/learn/certifications/exams/sc-200
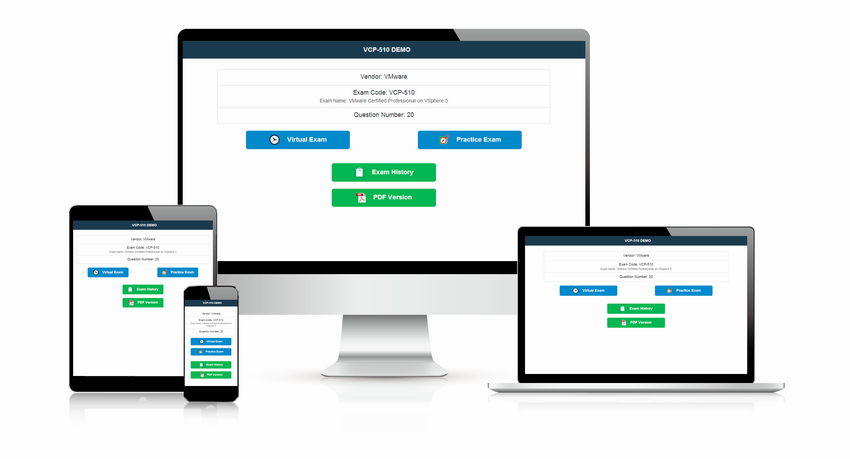
Free demo for your checking our products quality before buying
For those people who do not have the experience of taking part in exam, our SC-200 test training vce provide them a free chance to enjoy a small part of our products for free. They can check our Microsoft Certified: Security Operations Analyst Associate SC-200 valid practice questions before they decide to buy our products. Candidates can make the decision on whether they will buy our products or not after using our SC-200 test prep dumps. I can say it definitely that our products will bring a significant experience.
SC-200 test training vce are helpful for your Microsoft Microsoft Certified: Security Operations Analyst Associate certification which is the cornerstone for finding jobs. People who are highly educated have high ability than those who have not high education. The famous university is much stronger than normal university. But there is exception in this society. It is a huge investment when HR selected candidates, so Microsoft SC-200 test training torrent can help you stand out among countless candidates.

Our SC-200 exam valid questions give the candidates one-year free update
It is known that the exam test is changing with the times. Only by grasping the latest information about the examination, can the candidates get the SC-200 test practice vce more easily. We take actions to tackle this problem. The experts make efforts day and night to update the SC-200 latest training material with the first-hand information and latest news, you do not worry about the authority and accuracy of our Microsoft Certified: Security Operations Analyst Associate SC-200 latest study torrent.
Our SC-200 valid practice questions acquaint with the exam points
Our SC-200 test training vce can help the candidates know more about the examination. It has high accuracy of SC-200 questions and answers, since the experienced experts are in the high position in this field. Besides this advantage, our SC-200 free download pdf covers a wide range in this field and cover mostly 85% questions of the real test. We have devoted in this field for 9 years, so we have a lot of experiences in editing Microsoft Certified: Security Operations Analyst Associate SC-200 questions and answers.
Microsoft Security Operations Analyst Exam Certification Details:
| Sample Questions | Microsoft Security Operations Analyst Sample Questions |
| Books / Training | Course SC-200T00: Microsoft Security Operations Analyst |
| Duration | 120 mins |
| Exam Code | SC-200 |
| Schedule Exam | Pearson VUE |
| Passing Score | 700 / 1000 |
| Exam Name | Microsoft Certified - Security Operations Analyst Associate |
| Exam Price | $165 (USD) |
| Number of Questions | 40-60 |
SC-200 valid practice questions benefits the candidates
Our SC-200 : Microsoft Security Operations Analyst valid practice torrent mainly provide candidates complete and systematic studying materials. For those people who have been in company, the working ability is the key for boss to evaluate your ability. But for those people who are still looking for jobs, SC-200 free download pdf can prove their ability, especially for those people who do not have high education. So if want to find a good job and have a good living standard, our company SC-200 test prep vce is the best choice help you to achieve.
Microsoft SC-200 Exam Syllabus Topics:
| Section | Weight | Objectives |
|---|---|---|
| Mitigate threats using Microsoft Defender for Cloud Apps | 20-25% | - Investigate and respond to threats
|
| Mitigate threats using Microsoft Defender for Identity | 15-20% | - Hunt threats using Defender for Identity
|
| Mitigate threats using Microsoft 365 Defender | 25-30% | - Investigate and respond to threats in Microsoft 365 Defender
|
| Mitigate threats using Microsoft Defender for Endpoint | 25-30% | - Manage devices and monitor threats
|
Microsoft Security Operations Analyst Sample Questions:
You have an Azure subscription that contains an Azure logic app named app1 and a Microsoft Sentinel workspace that has an Azure AD connector. You need to ensure that app1 launches when Microsoft Sentinel detects an Azure AD-generated alert. What should you create first?
- A. a repository connection
- B. an automation rule
- C. awatchlist
- D. an analytics rule
Correct Answer: B 🗳️
Explanation: Only visible for Free4Torrent members. You can sign-up / login (it's free).
You have a Microsoft 365 subscription that uses Microsoft Defender for Endpoint Plan 2 and contains 500 Windows devices. As part of an incident investigation, you identify the following suspected malware files:
* sys
* pdf
* docx
* xlsx
You need to create indicator hashes to block users from downloading the files to the devices. Which files can you block by using the indicator hashes?
- A. File1.sys, File2.pdf, File3.dooc, and File4.xlsx
- B. File1.sys. File3.docx, and File4jclsx only
- C. File2.pdf. File3.docxr and File4.xlsx only
- D. File1.sysonly
- E. File1.sysand File3.docxonly
Correct Answer: A 🗳️
Explanation: Only visible for Free4Torrent members. You can sign-up / login (it's free).
You have a Microsoft Sentinel workspace.
You have a query named Query1 as shown in the following exhibit.
You plan to create a custom parser named Parser 1. You need to use Query1 in Parser1. What should you do first?
- A. Remove line 5.
- B. In line 3, replace the ' contains operator with the !has operator.
- C. In line 4. remove the TimeGenerated predicate.
- D. Remove line 2.
Correct Answer: A 🗳️
Explanation: Only visible for Free4Torrent members. You can sign-up / login (it's free).
You have a suppression rule in Azure Security Center for 10 virtual machines that are used for testing. The virtual machines run Windows Server.
You are troubleshooting an issue on the virtual machines.
In Security Center, you need to view the alerts generated by the virtual machines during the last five days.
What should you do?
- A. Modify the filter for the Security alerts page.
- B. Change the state of the suppression rule to Disabled.
- C. Change the rule expiration date of the suppression rule.
- D. View the Windows event logs on the virtual machines.
Correct Answer: B 🗳️
Explanation: Only visible for Free4Torrent members. You can sign-up / login (it's free).
You need to use an Azure Sentinel analytics rule to search for specific criteria in Amazon Web Services (AWS) logs and to generate incidents.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
a Microsoft 365 E5
Correct Answer:

Explanation:
Comprehensive and Detailed Explanation with all Microsoft Security Operations (SecOps) documents: = To search for specific criteria in Amazon Web Services (AWS) logs and generate incidents using Microsoft Sentinel, the configuration process follows a structured sequence according to Microsoft Sentinel documentation and the Azure Sentinel playbook for AWS integration.
Add the Amazon Web Services (AWS) connector
Before Sentinel can analyze AWS data, you must integrate AWS logs using the Amazon Web Services data connector. This connector streams AWS CloudTrail and other AWS log data into your Sentinel workspace.
Microsoft's documentation states:"Use the Amazon Web Services (AWS) connector to stream CloudTrail events and security logs into Microsoft Sentinel for analysis and alerting." Without this connector, Sentinel cannot query or detect AWS-specific activities.
Create a custom analytics rule that uses a scheduled query
Once data ingestion is established, you create an analytics rule in Sentinel using a scheduled query to continuously search for specific conditions (e.g., unauthorized access attempts, changes to VPC settings, etc.).
Microsoft specifies: "Custom analytics rules run KQL queries on a schedule to detect specific patterns or anomalies across ingested data sources." Set the alert logic After defining your rule, you configure the alert logic to determine when Sentinel should trigger an alert or incident. This includes setting thresholds, event frequency, severity levels, and entity mappings.
Microsoft Sentinel's official guidance notes: "Alert logic defines the conditions under which an alert is generated from the query results."
Viewing page 1 out of 87 pages.
Viewing questions 1-5 out of 435 questions.
Related Exam
Related Certifications
Over 62955+ Satisfied Customers
 1067 Customer ReviewsCustomers Feedback (* Some similar or old comments have been hidden.)
I have bought the SC-200 online test engine, from the customizable test, I can knew about all my weakness of the SC-200. So lucky, I passed exam with 94%.
Osmond
It has really helped me to raise my essay capabilities.It is my favorite testing engine for SC-200 exam.
Vic

I passed SC-200 exam with ease. The exam was easier than I thought. Do study the Microsoft SC-200 dumps thoroughly provided here 90% questions were from them.
Afra
I passed the exam with 92% score. Thank you Free4Torrent, I’ll recommend the resource to everyone in a similar situation.
Merle

I got 90% marks in the SC-200 certification exam. I studied for the exam from the pdf dumps by Free4Torrent. Amazing work. Suggested to all.
Hiram
Excellent SC-200 study braindumps to help pass the exam! I and my brother both passed yesterday! You can imagine how happy we are. Thank you so much! You are doing a wonderful job!
Isidore
The questions of the SC-200 are almost occurred in the actual test, so lucky, the answers are correct, so i pass it with high score.
Andrew
This SC-200 exam questions are so much valid, i passed my exam with the help of them today! All my thanks to you!
Vera
Many of the actual questions in the exam where identical to the SC-200 practice dumps here and it made me feel confident to pass the exam. Thanks!
Kent
The SC-200 dump questions are exactly the same as the real exam subjects.
Bradley
Questions and answers in the pdf file were almost the same as the real exam. Thank you for this great work Free4Torrent. I suggest all taking the SC-200 exam to prepare from this pdf file. I got 90% marks. Thanks
Walter
SC-200 practice dumps here are valid. Try them out, you won’t be disappointed. I just passed my exam last week.
Coral
The preparation was perfect for the curve ball questions that are planted in the SC-200 exam.
Miles
I have passed SC-200 exam with your material,so happy now.
Freda
After two unsuccessful attempts, I finally cleared my SC-200 certification exam. This time I relied on Free4Torrent only. Free4Torrent study guide equipped me with high score
Yves
I have clearedSC-200 exam. i come here just want to thank you.
Astrid
Quality and Value
Free4Torrent Practice Exams are written to the highest standards of technical accuracy, using only certified subject matter experts and published authors for development - no all study materials.
Tested and Approved
We are committed to the process of vendor and third party approvals. We believe professionals and executives alike deserve the confidence of quality coverage these authorizations provide.
Easy to Pass
If you prepare for the exams using our Free4Torrent testing engine, It is easy to succeed for all certifications in the first attempt. You don't have to deal with all dumps or any free torrent / rapidshare all stuff.
Try Before Buy
Free4Torrent offers free demo of each product. You can check out the interface, question quality and usability of our practice exams before you decide to buy.

The latest & valid real study questions with the verified answers can ensure you pass your actual test at first try. Download the free study torrent for your exam preparation and start study immediately. You will success with ease by our real questions.