Abundant kinds of exam materials to satisfy different studying habit
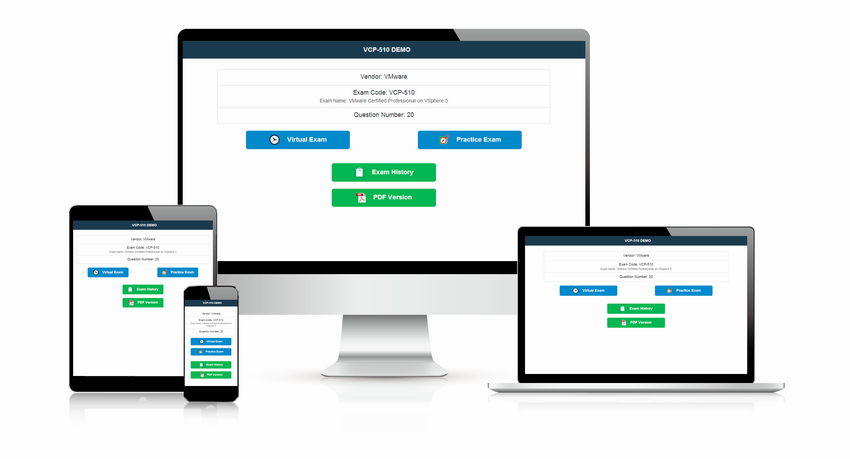
Many candidates notice that we have three choices for each CISM valid test questions: PDF, Soft test engine, APP test engine. In fact these three versions contain same questions and answers. Their different point is the way of presentation. PDF version of Certified Information Security Manager test vce pdf is the common style that many buyers may be used to this version if you want to print out and note on paper. Soft test engine of CISM valid test question is new version as software. It should be downloaded on computer first and then you can copy to any device, you can simulate the real test scene and use offline. APP test engine of Certified Information Security Manager latest study dumps have nearly same functions with Soft. It works based on browser. After download first, you can use offline too if you don't clear cache.
ISACA CISM Exam Certification Details:
With the wide use of computer more and more people want to enter into this industry, high-salary positions relating computer & network spring up. Certified Information Security Manager test training material: Certified Information Security Manager do help people enter into this field or have a nice promotion after passing exam and get professional certifications. That's why our CISM valid test questions are so popular and get so many high comments. If you are not satisfied with your recent jobs, our ISACA Certified Information Security Manager reliable training dumps can give you a chance to restart. IT certifications are regarded as important in most countries all over the world. Once you get a certification with our Isaca Certification Certified Information Security Manager latest study material, you may have chance to apply for an international large company or a senior position. It will bring you a better living condition with your job hopping. Our Certified Information Security Manager latest practice torrent benefit candidates in many aspects.

Exam details
ISACA CISM is used to be a manual exam, but over the years it has evolved into a Computer-Based Testing method, which ensures even more accuracy and reliability for its candidates. It is consisting of 150 questions that you need to clear within 240 minutes. This exam is available in various languages, such as Chinese, English, Japanese, Korean, and Spanish. It is held at the PSI testing centers around the world.
The exam voucher is valid for one year after it is released. For the ISACA members, the price of the CISM test is $575, but the non-members should pay $760. To pass this certification exam, an individual should score at least 450 points or higher.
Reference: https://www.isaca.org/credentialing/cism/cism-exam-content-outline
ISACA CISM: What resources should you use to prepare for the certification exam?
The CISM certification exam is not quite easy. You will have to make an effort in order to pass it. Even if you have significant competence in the industry, you must take the appropriate training. Thus, those professionals who have about 3-5 years of experience in the IS industry say that they needed two months of 3-4 hours a day learning and practicing in order to pass the test.
ISACA Information Security Manager Exam Syllabus Topics:
| Topic | Details | Weights |
|---|
| Information Risk Management | -Manage information risk to an acceptable level based on risk appetite in order to meet organizational goals and objectives. Task Statements - Establish and/or maintain a process for information asset classification to ensure that measures taken to protect assets are proportional to their business value.
- Identify legal, regulatory, organizational and other applicable requirements to manage the risk of noncompliance to acceptable levels.
- Ensure that risk assessments, vulnerability assessments and threat analyses are conducted consistently, at appropriate times, and to identify and assess risk to the organization’s information.
- Identify, recommend or implement appropriate risk treatment/response options to manage risk to acceptable levels based on organizational risk appetite.
- Determine whether information security controls are appropriate and effectively manage risk to an acceptable level.
- Facilitate the integration of information risk management into business and IT processes (e.g., systems development, procurement, project management) to enable a consistent and comprehensive information risk management program across the organization.
- Monitor for internal and external factors (e.g., key risk indicators [KRIs], threat landscape, geopolitical, regulatory change) that may require reassessment of risk to ensure that changes to existing, or new, risk scenarios are identified and managed appropriately.
- Report noncompliance and other changes in information risk to facilitate the risk management decision-making process.
- Ensure that information security risk is reported to senior management to support an understanding of potential impact on the organizational goals and objectives.
Knowledge Statements - Knowledge of methods to establish an information asset classification model consistent with business objectives.
- Knowledge of considerations for assigning ownership of information assets and risk.
- Knowledge of methods to identify and evaluate the impact of internal or external events on information assets and the business.
- Knowledge of methods used to monitor internal or external risk factors.
- Knowledge of information asset valuation methodologies.
- Knowledge of legal, regulatory, organizational and other requirements related to information security.
- Knowledge of reputable, reliable and timely sources of information regarding emerging information security threats and vulnerabilities.
- Knowledge of events that may require risk reassessments and changes to information security program elements.
- Knowledge of information threats, vulnerabilities and exposures and their evolving nature.
- Knowledge of risk assessment and analysis methodologies.
- Knowledge of methods used to prioritize risk scenarios and risk treatment/response options.
- Knowledge of risk reporting requirements (e.g., frequency, audience, content).
- Knowledge of risk treatment/response options (avoid, mitigate, accept or transfer) and methods to apply them.
- Knowledge of control baselines and standards and their relationships to risk assessments.
- Knowledge of information security controls and the methods to analyze their effectiveness.
- Knowledge of gap analysis techniques as related to information security.
- Knowledge of techniques for integrating information security risk management into business and IT processes.
- Knowledge of compliance reporting requirements and processes.
- Knowledge of cost/benefit analysis to assess risk treatment options.
| 30% |
| Information Security Governance | -Establish and/or maintain an information security governance framework and supporting processes to ensure that the information security strategy is aligned with organizational goals and objectives. Task Statements - Establish and/or maintain an information security strategy in alignment with organizational goals and objectives to guide the establishment and/or ongoing management of the information security program.
- Establish and/or maintain an information security governance framework to guide activities that support the information security strategy.
- Integrate information security governance into corporate governance to ensure that organizational goals and objectives are supported by the information security program.
- Establish and maintain information security policies to guide the development of standards, procedures and guidelines in alignment with enterprise goals and objectives.
- Develop business cases to support investments in information security.
- Identify internal and external influences to the organization (e.g., emerging technologies, social media, business environment, risk tolerance, regulatory requirements, third-party considerations, threat landscape) to ensure that these factors are continually addressed by the information security strategy.
- Gain ongoing commitment from senior leadership and other stakeholders to support the successful implementation of the information security strategy.
- Define, communicate, and monitor information security responsibilities throughout the organization (e.g., data owners, data custodians, end-users, privileged or high-risk users) and lines of authority.
- Establish, monitor, evaluate and report key information security metrics to provide management with accurate and meaningful information regarding the effectiveness of the information security strategy.
Knowledge Statements - Knowledge of techniques used to develop an information security strategy (e.g., SWOT [strengths, weaknesses, opportunities, threats] analysis, gap analysis, threat research)
- Knowledge of the relationship of information security to business goals, objectives, functions, processes and practices.
- Knowledge of available information security governance frameworks.
- Knowledge of globally recognized standards, frameworks and industry best practices related to information security governance and strategy development.
- Knowledge of the fundamental concepts of governance and how they relate to information security.
- Knowledge of methods to assess, plan, design and implement an information security governance framework.
- Knowledge of methods to integrate information security governance into corporate governance.
- Knowledge of contributing factors and parameters (e.g., organizational structure and culture, tone at the top, regulations) for information security policy development
- Knowledge of content in, and techniques to develop, business cases.
- Knowledge of strategic budgetary planning and reporting methods.
- Knowledge of the internal and external influences to the organization (e.g., emerging technologies, social media, business environment, risk tolerance, regulatory requirements, third-party considerations, threat landscape) and how they impact the information security strategy.
- Knowledge of key information needed to obtain commitment from senior leadership and support from other stakeholders (e.g., how information security supports organizational goals and objectives, criteria for determining successful implementation, business impact).
- Knowledge of methods and considerations for communicating with senior leadership and other stakeholders (e.g., organizational culture, channels of communication, highlighting essential aspects of information security).
- Knowledge of roles and responsibilities of the information security manager.
- Knowledge of organizational structures, lines of authority and escalation points.
- Knowledge of information security responsibilities of staff across the organization (e.g., data owners, end-users, privileged or high-risk users)
- Knowledge of processes to monitor performance of information security responsibilities.
- Knowledge of methods to establish new, or utilize existing, reporting and communication channels throughout an organization.
- Knowledge of methods to select, implement and interpret key information security metrics (e.g., key performance indicators [KPIs] or key risk indicators [KRIs]).
| 24% |
| Information Security Incident Management | -Plan, establish and manage the capability to detect, investigate, respond to and recover from information security incidents to minimize business impact. Task Statements - Establish and maintain an organizational definition of, and severity hierarchy for, information security incidents to allow accurate classification and categorization of and response to incidents.
- Establish and maintain an incident response plan to ensure an effective and timely response to information security incidents.
- Develop and implement processes to ensure the timely identification of information security incidents that could impact the business.
- Establish and maintain processes to investigate and document information security incidents in order to determine the appropriate response and cause while adhering to legal, regulatory and organizational requirements.
- Establish and maintain incident notification and escalation processes to ensure that the appropriate stakeholders are involved in incident response management.
- Organize, train and equip incident response teams to respond to information security incidents in an effective and timely manner.
- Test, review and revise (as applicable) the incident response plan periodically to ensure an effective response to information security incidents and to improve response capabilities.
- Establish and maintain communication plans and processes to manage communication with internal and external entities.
- Conduct post-incident reviews to determine the root cause of information security incidents, develop corrective actions, reassess risk, evaluate response effectiveness and take appropriate remedial actions.
- Establish and maintain integration among the incident response plan, business continuity plan and disaster recovery plan.
Knowledge Statements - Knowledge of incident management concepts and practices.
- Knowledge of the components of an incident response plan.
- Knowledge of business continuity planning (BCP) and disaster recovery planning (DRP) and their relationship to the incident response plan.
- Knowledge of incident classification/categorization methods.
- Knowledge of incident containment methods to minimize adverse operational impact.
- Knowledge of notification and escalation processes.
- Knowledge of the roles and responsibilities in identifying and managing information security incidents.
- Knowledge of the types and sources of training, tools and equipment required to adequately equip incident response teams.
- Knowledge of forensic requirements and capabilities for collecting, preserving and presenting evidence (e.g., admissibility, quality and completeness of evidence, chain of custody).
- Knowledge of internal and external incident reporting requirements and procedures.
- Knowledge of post-incident review practices and investigative methods to identify root causes and determine corrective actions.
- Knowledge of techniques to quantify damages, costs and other business impacts arising from information security incidents.
- Knowledge of technologies and processes to detect, log, analyze and document information security events.
- Knowledge of internal and external resources available to investigate information security incidents.
- Knowledge of methods to identify and quantify the potential impact of changes made to the operating environment during the incident response process.
- Knowledge of techniques to test the incident response plan.
- Knowledge of applicable regulatory, legal and organization requirements.
- Knowledge of key indicators/metrics to evaluate the effectiveness of the incident response plan.
| 19% |
| Information Security Program Development and Management | -Develop and maintain an information security program that identifies, manages and protects the organization’s assets while aligning to information security strategy and business goals, thereby supporting an effective security posture. Task Statements - Establish and/or maintain the information security program in alignment with the information security strategy.
- Align the information security program with the operational objectives of other business functions (e.g., human resources [HR], accounting, procurement and IT) to ensure that the information security program adds value to and protects the business.
- Identify, acquire and manage requirements for internal and external resources to execute the information security program.
- Establish and maintain information security processes and resources (including people and technologies) to execute the information security program in alignment with the organization’s business goals.
- Establish, communicate and maintain organizational information security standards, guidelines, procedures and other documentation to guide and enforce compliance with information security policies.
- Establish, promote and maintain a program for information security awareness and training to foster an effective security culture.
- Integrate information security requirements into organizational processes (e.g., change control, mergers and acquisitions, system development, business continuity, disaster recovery) to maintain the organization’s security strategy.
- Integrate information security requirements into contracts and activities of third parties (e.g., joint ventures, outsourced providers, business partners, customers) and monitor adherence to established requirements in order to maintain the organization’s security strategy.
- Establish, monitor and analyze program management and operational metrics to evaluate the effectiveness and efficiency of the information security program.
- Compile and present reports to key stakeholders on the activities, trends and overall effectiveness of the IS program and the underlying business processes in order to communicate security performance.
Knowledge Statements - Knowledge of methods to align information security program requirements with those of other business functions
- Knowledge of methods to identify, acquire, manage and define requirements for internal and external resources
- Knowledge of current and emerging information security technologies and underlying concepts
- Knowledge of methods to design and implement information security controls
- Knowledge of information security processes and resources (including people and technologies) in alignment with the organization’s business goals and methods to apply them
- Knowledge of methods to develop information security standards, procedures and guidelines
- Knowledge of internationally recognized regulations, standards, frameworks and best practices related to information security program development and management
- Knowledge of methods to implement and communicate information security policies, standards, procedures and guidelines
- Knowledge of training, certifications and skill set development for information security personnel
- Knowledge of methods to establish and maintain effective information security awareness and training programs
- Knowledge of methods to integrate information security requirements into organizational processes (e.g., access management, change management, audit processes)
- Knowledge of methods to incorporate information security requirements into contracts, agreements and third-party management processes
- Knowledge of methods to monitor and review contracts and agreements with third parties and associated change processes as required
- Knowledge of methods to design, implement and report operational information security metrics
- Knowledge of methods for testing the effectiveness and efficiency of information security controls
- Knowledge of techniques to communicate information security program status to key stakeholders
| 27% |
Our superior service is the key factor why we stand out
We hold the opinion that customer is the first. So we offer 24 hours online service so that buyers can obtain assist from us about Certified Information Security Manager valid test questions: Certified Information Security Manager any time. Even on large holidays and at nigh we arrange professional service staff on duty. Besides, we bring out worry-free shopping. If you are interested in our CISM valid test questions, purchasing process is easy. You can pay by your credit card and instant download within 10 minutes. If you worry about the quality of our latest ISACA Certified Information Security Manager latest practice dumps, we also provide a small part of our complete files as free demo for your reference before buying. "Money back guarantee" is our promise which will make buyers safe.
All in all, if you are still looking for the best products to help you clear exam and obtain your dreaming certification, choosing our Certified Information Security Manager latest practice torrent will be your best select.
Instant Download: Upon successful payment, Our systems will automatically send the CISM dumps you have purchased to your mailbox by email. (If not received within 12 hours, please contact us. Note: don't forget to check your spam.)
Purchasing our high-quality products get high passing score
Our Certified Information Security Manager test vce pdf win a good reputation from candidates for its highly passing quality. We have special channel to get latest exam data and relating news so that our professional educators can work out high-quality questions and answers of Isaca Certification CISM valid test questions: our 99% passing-rate products will bring your confidence in your exam. Based on our past experience and data, if you pay close attention our Certified Information Security Manager reliable training dumps, only one or two days' preparation will make you enough skilled for your real test. If you spend much time on our CISM valid test torrent, you will get a wonderful passing score even beyond your expectation.
 Felix


 Alfred
 Elaine
 Kenneth
 Marsh

 Tyler

 Matt
 Rachel
 Ford
 Humphrey
 Sabrina